2009年9月23日星期三

[转贴]黑客技术:网络入侵一般步骤及思路

[转贴]黑客技术:网络入侵一般步骤及思路

%ef%bc%bb%e8%bd%ac%e8%b4%b4%ef%bc%bd%e9%bb%91%e5%ae%a2%e6%8a%80%e6%9c%af%e7%bd%91%e7%bb%9c%e5%85%a5%e4%be%b5%e4%b8%80%e8%88%ac%e6%ad%a5%e9%aa%a4%e5%8f%8a%e6%80%9d%e8%b7%af

zkheartboy's Linux life是个很不错的站点,经常会登出一些很有价值的文章出来,在此分享一篇最新文章,是关于网络入侵方面的。

===

第一步:进入系统

1. 扫描目标主机。

2. 检查开放的端口,获得服务软件及版本。
3. 检查服务软件是否存在漏洞,如果是,利用该漏洞远程进入系统;否则进入下一步。

4. 检查服务软件的附属程序(*1)是否存在漏洞,如果是,利用该漏洞远程进入系统;否则进入下一步。

5. 检查服务软件是否存在脆弱帐号或密码,如果是,利用该帐号或密码系统;否则进入下一步。

6. 利用服务软件是否可以获取有效帐号或密码,如果是,利用该帐号或密码进入系统;否则进入下一步。

7. 服务软件是否泄露系统敏感信息,如果是,检查能否利用;否则进入下一步。

8. 扫描相同子网主机,重复以上步骤,直到进入目标主机或放弃。

第二步:提升权限

1. 检查目标主机上的SUID和GUID程序是否存在漏洞,如果是,利用该漏洞提升权限,否则进入下一步。

2. 检查本地服务是否存在漏洞,如果是,利用该漏洞提升权限,否则进入下一步。

3. 检查本地服务是否存在脆弱帐号或密码,如果是,利用该帐号或密码提升权限;否则进入下一步。

4. 检查重要文件的权限是否设置错误,如果是,利用该漏洞提升权限,否则进入下一步。

5. 检查配置目录(*2)中是否存在敏感信息可以利用。

6. 检查用户目录中是否存在敏感信息可以利用。

7. 检查临时文件目录(*3)是否存在漏洞可以利用。

8. 检查其它目录(*4)是否存在可以利用的敏感信息。

9. 重复以上步骤,直到获得root权限或放弃。

第三步:放置后门

最好自己写后门程序,用别人的程序总是相对容易被发现。

第四步:清理日志

最好手工修改日志,不要全部删除,也不好使用别人写的工具。

附加说明:

*1 例如WWW服务的附属程序就包括CGI程序等

*2 这里指存在配置文件的目录,如/etc等

*3 如/tmp等,这里的漏洞主要指条件竞争

*4 如WWW目录,数据文件目录等

/***************************************************************************** /

好了,大家都知道了入侵者入侵一般步骤及思路 那么我们开始做入侵检测了。

第一步

我们都知道一个入侵者想要入侵一台服务器首先要扫描这台服务器,搜集服务器的信息,以便进一步入侵该系统。系统信息被搜集的越多,此系统就越 容易被入侵者入侵。所以我们做入侵检测时,也有必要用扫描器扫描一下系统,搜集一下系统的一些信息,来看看有没有特别流行的漏洞(呵呵这个年头都时兴流行 哦:)

第二步

扫描完服务器以后,查看扫描的信息---->分析扫描信息。如果有重大漏洞---->修补(亡羊补牢,时未晚),如果没有转下一步。

第三步

没有漏洞,使用杀毒工具扫描系统文件,看看有没有留下什么后门程序,如:nc.exe、srv.exe……如果没有转下一步。

第四步

入侵者一般入侵一台机器后留下后门,充分利用这台机器来做一些他想做的事情,如:利用肉鸡扫描内网,进一步扩大战果,利用肉鸡作跳板入侵别的网段的机器,嫁祸于这台机器的管理员,跑流影破邮箱……


2009年9月19日星期六

Why OpenVZ and not XEN.

Why OpenVZ and not XEN.

After one year of operation with XEN, I chosed to move Fridu from XEN paravirtualization, to OpenVZ container model. Here after some explanations on the why of this change and the description of my new architecture.

Table of Content

Disclaimer

Anything I wrote here was done outside of my professional work context and  none of my current/past employers/customers have participate or even be consulted for this work. Fridu is 100% part of my free time, and everything including hosting is funded on our pocket money and used to support non commercial friend organisations. While I think I have the technical background to design a smart architecture (cf:my profile). I nevertheless do not garanty that it will work for you, or even that you will agree with me. I still hope it may help some of you and I would be more than happy to incorporate improvement if ever you have some.

Demonstration/Video

This demonstrations is a live screencast done with xvidcap on Linux, it shows how to create a new virtual machine through Proxmox OpenVZ web graphic interface, and then shows how to expose the newly created zone to the outside world with three different mechanisms: vpn, port forwarding and reverse proxy. Demo run for about 25mn, its using video flash and hopefully runs smootly on any plateform.

My ISP new OpenVZ architecture

The new Fridu architecture is very similar to the old Fridu-XEN, it uses the same firewall and provides the same networking port forwarding facilities and leverage OpenVPN for direct access to virtual machines. The only changes are the transfert from Xen to OpenVZ and the introduction of a reverse proxy at hypervisor level.


Xen is rock solid, but ...

I had no issues with XEN functionalities or stability. I never had to reboot any zones and shut down my system with 360days of update time, which mean XEN never went down from the time I switched on my system on, to the time I moved to a new dedicated server with OpenVZ. My Xen config is described in following post (here).

I nevertheless have two main reproach to Xen, the first one is that it locks physical RAM and thus requirer RAM that I do not have on my cheap dedicated server. The second one is that XEN to XEN networking is extremely slow, which is in fact the only MUST solve problem I see to Xen.  

OpenVZ limited but light weight and simple.

OpenVZ has one strong limit compare to XEN, it is not a full visualization and  therefore you're limited to Linux only containers. People working with Sun will recognize Solaris zones concept, that was introduced few years ago. Like for Solaris every OpenVZ zones shared the same kernel, which at OVH translate in a Linux-2.6.24.7 kernel. This being said, it is important to understand that Linux distributions are independent of kernel, you can therefore run any Linux distributions you want under a unique kernel. While OVH ships Debian Etch with OpenVZ hyperviseur, you can chose any other distribution for your zones, new version of Fridu mostly operated with Ubuntu, but nothing prevents you from running multiple distributions. OVH ships template for Debian, CentOS, Gentoo and Ubuntu, but if this is not enough you can either create your own template or download one from Internet (OpenVz-WIKI)

OpenVZ includes a set of scripts to create/manage virtual machines, unlike Xen that is shipped naked and where I had to write more or less equivalent scripts by myself (cf: Fridu Xen Quick Start). Furthermore  OVH ships OpenVZ with a web console from Proxmox, not that I'm a big fan of having a GUI, but as you can see on the video, it is great to make sexy demos.This console allows you to create a new virtual instances literally in a mater of seconds :) It allows you to start/stop change ram size, IP adresses, etc. on any instances without forcing you to remember any special commands. While Proxmox console misses few features like an SSH applet, a firewall config, or a java VPN. I must say that I get used to it and create every virtual machine through the web GUI.

OpenVZ is very light weight, not only it shares the same kernel, but also the same filesystem and networking stack. Direct result is that, on a given server you can run more OpenVZ zones than you could run XEN virtual-machines. From a user point of view when a zone is up, wether you run OpenVZ or XEN is fairly transparent, this being said they are nevertheless some fundamental differences:

  • OpenVZ ram is taken from hypervisor global pool (RAM+Swap), when Xen takes RAM from hypervisor physical ram and handles its private swap by virtual machines. Direct result is that with OpenVZ you can allocate more RAM that you effectly have, on the other hand if one zone lack RAM your zone will not expend on swap. In fact OpenVZ refuses to allocate RAM to requesting process, which for most of them translates in a core dump :( As swaping is never a good idea, both methods could finaly look more or less equivalent, this being said the small advantage of OpenVZ strategy is that it is easier to share unused RAM in between differents zones, which may have some important for cheap hosting configuration where RAM is limited.
  • OpenVZ zones and hyperviseur share the same kernel, as a result some functions fails (ex: changing system time) while this should not be an issue, it breaks more scripts than it should :(
  • No boot console is a real bad point for OpenVZ. It makes template creation complex. In fact you have no idea of what happen until you can access to your system, which obvisouly never happen when boot fail :( The fact you can access any given zone logs directly from the hyperviseur through /vz/private/zone-id directory makes debug possible, but far less simple than with a full boot console as provided by Xen. Note that some distributions like Debian will write into your VM /var/log/init.log the trace of your boot sequence, unfortunatly this is not working on ever distribution, Ubuntu being one of them.
  • A snoopable network interface, this is a very good point for OpenVZ. While Xen also allows to snoop your network interface with TCPdump or Wireshark, Solaris zones does not support it. Snooping network  interfaces is a key feature for debugging any network infrastructure and almost mandatory to understand what happen when your hosting configuration is not working.
  • A share filesystem, the main advantage is that you can access directly to any zone private disk from the hypervisor, the limit is that you cannot leverage a SAN interface directly from the zone as under xen with ISCSI. This being said for cheap hosting OpenVZ option is a better choice.
  • Proxmox web GUI, while this is not OpenVZ as it, it is shipped standard and allows you to create/manage your virtual machines in a very nice and intuitive way.Further more Proxmox provide a list of appliances that you can download from ftp://pve.proxmox.com/appliances this allow you to install drupla, joomla as well as many other nice tool in a mater of seconds, nice isn't it ?

Fridu OpenVZ networking config

I reused the exact same firewall I had with XEN, did not even change one line from previous script. Nevertheless this time I used a more simple configuration with only one security zone, and  added of a reverse proxy (pound) for http port redirection on the adequate virtual machine.

OpenVZ hypervisor runs firewall rules for port firtering and forward to any service of a given zone and pound reverse proxy is handling http, redirecting get/post to the adequate web server. Note that if I had more public IP adresse I could get rid of my reverse proxy, but I use a cheap OVH plan (kimsiffi) which only provide two public IPs.

You can find detail options about Fridu Firewall  (here) my current config is somehow simple and explained here after.

Security zones: OpenVZ default config provides one virtual network interface (vnet0) at the hypervisor level. While this does not enforced strong isolation in between zones, you can nevertheless select a given outgoing IP adress from internal submask, which hopefully should be more than enough for most of us.

Here after an extract from my Firewall config, with my two public IP adresses. Both zones share the same internal (vnet0) and external (eth0) network interfaces. The only difference comes from internal network submasks 10.10.101/10.10.102.

# Zones definition
# -----------------
IP_ONE=91.121.173.80
IP_TWO=87.98.139.141

CreateZone NAME=zOne   NIC=eth0 EXT=$IP_ONE BR=venet0 INT=10.10.101.0 MASK=255.255.255.0
CreateZone NAME=zTwo   NIC=eth0 EXT=$IP_TWO BR=venet0 INT=10.10.102.0 MASK=255.255.255.0
 

Right after zone definition, comes the hypervisor network configuration. The hypervisor is in a special zone named "none". As it has direct access to external network interface (eth0) port forwarding is unnecessary and we only define port filtering is required. In my config, I need to open:

  • Port TCP/22 for SSH
  • Port TCP/80 and 443 for HTTP/HTTPS
  • Port 5900 is used by VNCterm to provide console thought VNC applet.
  • Port UDP/44096 andTCP/453 for OpenVPN
# Application Port & Forwarding (default ACCEPT = none)
# ------------------------------------------------------
CreateApp  NAME=DOM0_SSH       ZONE=none      EXT=tcp:22        INT=eth0 ;# ssh Fridu.net goes to dom0
CreateApp  NAME=DOM0_WWW     ZONE=none      EXT=tcp:80        INT=eth0 ;# https need for promox console
CreateApp  NAME=DOM0_SSL       ZONE=none      EXT=tcp:443      INT=eth0 ;# https need for promox console
CreateApp  NAME=DOM0_VNCt     ZONE=none      EXT=tcp:5900     INT=eth0 ;# Virtual Machine console through VPNc
CreateApp  NAME=DOM0_VPNt     ZONE=none      EXT=tcp:563       INT=eth0 ;# OpenVPN in TCP
CreateApp  NAME=DOM0_VPNu    ZONE=none      EXT=udp:44096 INT=eth0 ;# check User Custom Rules later 

The last mandatory part of firewall rules is how to forward port to a designated virtual machine. For example mapping SSH port (tcp/22) to a external port (ex:tcp/2215) to allow the administrator to access to a given machine without passing thought the VPN.  In following configuration extract we see how I redirect mail SMPT/IMAP traffic, as well as HTTP (Apache/Tomcat) or SSH. With following configuration a "ssh -p 2215 root@my-pubic-ip" will connect  to ssh port 22 on virtual machine 10.10.101.5, and an http://my-public-ip:815 will connect on my tomcat instance on 10.10.101.5, etc.

# map external mail SMPT to Mail zone port 2525 to seperate from local traffic that arrive through VPN on port 25
CreateApp  NAME=Mail_SMTP   ZONE=zOne    EXT=tcp:25      INT=10.10.101.1:2525
CreateApp  NAME=Mail_IMAP   ZONE=zOne    EXT=tcp:993     INT=10.10.101.1:993
 
# Any traffic coming from IP-TWO/port 80 is redirected to 10.10.102.2
CreateApp  NAME=Domi_WEB    ZONE=zTwo    EXT=tcp:80      INT=10.10.102.2:80
 
# Allow SSH and HTTP direct mapping for 10.10.101.5
CreateApp  NAME=SSO_SSH    ZONE=zOne    EXT=tcp:2215     INT=10.10.101.5:22
CreateApp  NAME=SSO_WWW    ZONE=zOne    EXT=tcp:8015     INT=10.10.101.5:80
CreateApp  NAME=SSO_TOM    ZONE=zOne    EXT=tcp:8115     INT=10.10.101.5:8180

While Fridu Firewall will do the job with only previous rules, you may want to add some extra rules to optimize your configuration.  Three set of rules in my custom optimization section:

  • FTP one is only required if you want FTP to work in passive mode, which is often the case.
  • Second one is almost mandatory, (tun+/vnet+) allow VPN to reach any zone directly, while (vnet+/vnet+) allows zone to zone connection. If you run a share VPN you MUST have tun+/vnet+, while vnet+/vnet+ might only be needed if one zone runs a service shared by other, example LDAP, DNS, ...
  • Last one is an hugely hack that allow my TCP vpn on port 563 to be viewed as sitting on port 443 when targeting my IP-TWO. This allow me to have HTTPS/IP-ONE and VPN/IP-TWO when both share the same port and the same external interface (eth0)
# User Before/After Zone Custom Tables (before-input|output|forwarding, after-input|...)
# ----------------------------------------------------------------------------------
if test "$ACTION" = "start" ; then
  # DoIt modprobe  -s ip_conntrack_ftp                                    # load FTP session tacking

  # we're not a bank make our life simple
  DoIt iptables  -A after-forwarding -i venet+ -o venet+  -j ACCEPT   # allow VM to talk together
  DoIt iptables  -A after-input      -i tun+    -j ACCEPT               # allow VPN talk to dom0
  DoIt iptables  -A after-forwarding -i tun+    -o venet+  -j ACCEPT   # allow VPN talk to zones
  DoIt iptables  -A after-forwarding -i venet+ -o tun+     -j ACCEPT   # allow Zones talk to VPN

  # Make SSL on IP-two to be redirected on port 563
  DoIt iptables  -A PREROUTING -t nat -i eth0 --destination 87.98.139.141 --proto tcp --dport 443 -j DNAT --to 91.121.173.80:563

fi

Download Fridu firewall

Fridu firewall has been extended to support not only OpenVZ but also XEN or VirtualBox and has now its dedicated page.

My Reverse proxy configuration.

One change with my previous architecture is the addon of a reverse proxy, while no mandatory this add a lot of flexibility.  I found pound to be exactly what I needed. While pound is originally more target to be use as a load balancer, fail over and SSL end point, it works very well as a generic proxy.Pound is part of standard distribution and thus a simple "apt-get install pound" is enough to get it run. While documentation is very limitted, the configuration file remains simple enough for this not to be an issue.

  • 1st define a listen IP-ADDR/Port for your reverse proxy
  • 2nd define your services, with as input your DNS name as known by external internet users,  and as output your OpenVZ internal zone + port.
In following config sample, my pound wait on interface 91.121.173.80 (Fridu public addres) port 80. It then forwards any http request with destination "www.fridu.net" to virtual machine named into the hypervisor /etc/hosts "vz-opensso" on port 8180, and request to zxid.fridu.net to the same virtual machine but on port 81.

## redirect all requests on port 8080 ("ListenHTTP") to the local webserver (see "Service" below):
ListenHTTP
        Address 91.121.173.80
        Port    80

        # my services definition

        Service
                HeadRequire "Host:.*www.fridu.net.*"
                BackEnd
                        Address vz-opensso
                        Port    8180
                End
        End

        Service
                HeadRequire "Host:.*zxid.fridu.net.*"
                BackEnd
                        Address vz-opensso
                        Port    81
                End
        End
End

Dnsmaq a small domain named server.

Running a local DNS name server is not mandatory it is nevertheless very convenient to have your VMs being able to use local name of others VMs. For such a small usage a full dns like "bind9" is useless and "dnsmasq" is what we need. When running "dnsmasq" on your hypervisor, it will reads your "/etc/hosts"  and serve it to every VMs, any other request are forward to the DNS defined in "/etc/resolv.conf" . As a result "dnsmasq" config is minimal, you only have to define which interface you listen and your default domain extention.

 root@ks362337:~# cat /etc/dnsmasq.conf
# Configuration file for dnsmasq.
# "/usr/sbin/dnsmasq --help" or "man 8 dnsmasq" for details.

# Domain anything you want but "local" or client will request mdns
domain=vpn
expand-hosts

# Never forward names without a dot or domain part
bogus-priv

# /etc/resolv.conf is static, no monitoring needed
no-poll

# Do not listen eth0
except-interface=eth0

Last but not least you need your VMs to point on your local DNS, which is hopefully your template default.

root@vz-fulup:~# cat /etc/resolv.conf
search ovh.net
nameserver YOUR_HYPERVISOR-IP
nameserver 127.0.0.1

OpenVPN

While being optional I highly recommend OpenVPN for such an architecture, it is an easy to install product and it significantly simplify administrator and developer task. OpenVPN is available out of the box with any distribution. Fridu configuration is avaliable (here)

Proxmox web frontend console

Proxmox's web frontend is not a native component of OpenVZ, nevertheless it is a very useful companion, and I deeply recommend to who ever is willing to adopt OpenVZ, to concider Proxmox. If you're not convinced check my small video demo.

For most of it its Proxmox usage is strait forward. The only issue I had was with the embedded vnc java applet that provides a vt100 entry point to virtual machines. While on the browser side Proxmod uses a traditional vncviewer on the server side it uses vncterm. I use VNC frequently, but  never seen vncterm before. Vncterm is a contribution from Proxmox to VNC, it is small vt100 emulation that can be render remotely thought a vncviewer, and does not requirer X11 to be installed on the machine.

When clicking in your browser on the "console" tab of your Proxmox GUI, it starts a vncterm process in your hypervisor. Note that because vncterm is started at the hypervisor level, neither you need vncterm to be installed in each virtual machines, neither you need a working network on targeted VM. If you check your huperviser process after click in console you should see.

ps -ef | grep vncterm
/usr/bin/vncterm -rfbport 5900 -passwdfile rm:/tmp/.vncpwfile.7355 -timeout 1 -c /usr/sbin/vzctl enter 101
 
The only bad news is that vncterm does not leverage any well known ports as tcp:22 or tcp:443, in fact it takes any available port on the hypervisor in range 5900-6000. This mean that you need at least to have port 5900 open on the hypervisor, having only one port (5900) should allow you to have one active vncterm active at a time.

A big thank to  Dietmar from Proxmox who provided me with a very quick and very efficient support.

Limitations, bugs and tips.

Limitations/ bugs.

I did not found any significant bugs on OpenVZ, nevertheless Ubuntu template as shipped by OVH need following fix, or SSH from within a template will not work. My system is up and running since summer and I never had any trouble. The only few things I do after each zone creation is to add two missing quite useful pseudo devices, update my /etc/hosts and add required packages with apt-get.

  • No /dev/tty           -> "vzctl exec MY-VIRTUAL-MACHINE-ID mknod /dev/tty c 5 0"
  • No /dev/random -> "vzctl exec MY-VIRTUAL-MACHINE-ID mknod /dev/random c 1 8"
  • No /dev/console

Tips:

  • When checking processes list on the hypervisor with "ps -ef" you see every processes, including the one running on VMs. As a result a "pkill -9 apache2" at hypervisor level will kill every single apache running on every VMs. Needs to be know Cool
  • If a VM restart fails (ex: you messed up network config, break some init script, not enough RAM, ....). While obviously you cannot log on your broken VM !!! You can still try to enter the VM from the hypervisor with "vzctl enter VM-ID" command. Example: your "syslogd" did not start, as this the1st process to be started by init-rc, it locks everything else and especially "sshd" which is usually the second one to be started. As you have no SSHD you cannot connect with SSH, obvious isn't it ? You can then use the "vzctl enter VM-ID" doing a "ps -ef" you should see a pocess like "/etc/init/rc 2" as init is not finished. You can then restart your syslogd with "/etc/init.d/sysklogd" or what ever is necessary to fix your problem.
  • if you can reach a VM from the outside, but cannot reach internet from that VM, then you need to check your "CreateZone" rule.  Double check that your network mask is compliant with your VM local IP adresse.  Example (createZone ... EXT=IP1  INT=10.10.1.0 MASK=255.255.255.0) will map any VMs with local IP 10.10.1.xxx in IP1, when (createZone ... EXT=IP2  INT=10.10.1.2 MASK=255.255.255.255) will only map 10.10.1.2 inside IP2. Note network differences with MASK and INT with/without zero at the end. Zone network mask defines outgoing policies, and a wrong definition will not impact incoming requests, but will prevent outgoing requests to work.
  • when learning how to handle multiple public IP addresses, to forward a dedicated intenet port  from a specific pubic IP to an internal VM's IP/port, do not start with port "22" but with something less critical like 80 or 25. An error on port "22" may prevent SSH access to your hypervisor, forcing you to reboot your full server to gain back SSH access. The other good practice is to launch a batch that will stop your firewall automatically after 10mn "(sleep 600; Fridu-firewall.script stop)&  Fridu-firewall.script start)" like than even if you kill your SSH access, it is only for 10mn Innocent

Contact me.

Please let's your comment, and if you find any bug or improvement please let me know.


Comments (12)
Thank you it was good 20 minutes
12 Wednesday, 02 September 2009 18:28
Ivan
Thank you! It was very intresting presentation, and I hope will give it a try.
Waitig for new interestiong matirials.
How to check how much traffic OpenVZ VMs are using?
11 Saturday, 13 June 2009 20:42
Tom
1)How can we see how much traffic OpenVZ VMs are using?
2)How can we see how much traffic Xen VMs are using?
===> Fulup respond
Never really search for this information, but I don't see why ntop http://www.ntop.org should not work.
Super demo de Proxmox
10 Tuesday, 09 June 2009 17:34
Jean
Seulement te remercie pour partager tes conaissances de linux, et en ce cas de Proxmox. Cette Demo m'a été vraiment interesante pour comprendre la base de la virtualization.

Merci beaucoup.
your firewall video
9 Tuesday, 19 May 2009 23:30
j jammer
Very insightful. Thank you.. although I may watch it one or two more times it is extremely helpful in understanding the methodology of setup.
What about OpenVPN?
8 Wednesday, 06 May 2009 13:58
nicolas
Hi Fulup,
Many Thanks for your fast reply on my previous post. I was wandering about your OpenVPN usage in such an architecture.
Could you tell me if I'm wrong? Basically your openVPN usage in such an architecture saves you from one SSH to your hypervisor before being able to SSH your zones ?
I mean, thanks to OpenVPN, you connect to your zone directly from your remote workstation. If I do not install OpenVPN, all I need to get the same result is to first connect in SSH to your supervisor using the public IP address (port-SSH) and from then I get the possibility to SSH any zones running onto the supervisor.
Did I mist something and are there other interests of using a VPN connection in such an architecture?
PS: Sorry if it's a stupid question. I'm not an expert and I try to simplify the architecture as much as possible without loosing intersest of tool you introduced through this page. I'm BTW going to setup a similar architecture in the coming weeks.
Thanks in advance and congratulation for your very interesting topics
Nicolas
=========== Fulup respond ========
OpenVPN save you more than one SSH port. If SSH is the only issue, you should use portforwarding to a given VZ bypassing the hypervisor. Now with OpenVPN you get access to any port of your VZ, which is equivalent of having a new machine attache to your local network.
Nice tutorial / Little question
7 Tuesday, 05 May 2009 15:10
Nicolas
Hi Fulup,
Thanks very much for this nice tutorial. It really helps understanding your architecture.
I have a question regarding the usage of the reverse proxy. Technically speaking, why not using the ip failover supplied by OVH instead. Why not simply assigning an IP failover to each virtual machine for delivering the requested services to the internet?
This question comes because I"ll probably set up such an environment on a dedicated EG or MG model from OVH. These infrastructure is supplied with some free extra ip failover. I was just wandering what was the difference of the two solutions in term of security, performance or whatever.
Best Regards, Nicolas
=========== Fulup Respond =========
You make a perfectly valid comment, at fridu we only have one fail-over IP, but I use it for exact purpose, it points to a special VZ. If you point one full zone toward a given virtual machine, it achieves exactly what you describe. From a performance and security point of view it is equivalent.
Changing IP address of Virtual Machine
6 Thursday, 26 February 2009 16:52
Ap.Muthu
The ProxMox v1.1 GUI allows change of IP of the host machine. How do we change the iP address of a VM created using the templates like Joomla!, etc. Also how is it done for stabdard CentOS 4/5 installs.
While creating the VM say Joomla, we assign 192.168.10.1 instead of the default 127.0.0.1, we see it assigned to venet0:0 in the outpuit of the ifconfig command. Even setting another IP in a new file called etc/network/interfaces.new and restarting the VM does not set it and the it still shows the old IP only.
===== Fulup Respond =====
This is unfortunately for you out of scope. Fridu firewall is independent from how Joomla/OpenVZ handle IP addresses.This being said if you change any IP within your internal virtual network, you MUST update your Firewall or nothing will work anymore, nevertheless and despite of this, you might be interested to know that fridu.org run Joomla within a Proxmox/OpenVZ container.
Informative and insightful.
5 Monday, 23 February 2009 11:24
wese
I'm using OpenVZ now for 2 Years and was using KVM to run Windows when i was testing some stuff.
Although a great writeup with lots of information for virtualization beginners.
On thing i found out over the time, when you have an high traffic server it's better to put it directly into the internet, if you got more ip addresses available, because the dnat seems to slowdown a little, and setup iptables inside the VE.
- wese
========== Fulup respond =============
I've trouble to understand how IPTABLES could slow down your connectivity. At least with a 100Mbit/s connectivity, I do not see any bottle neck created by routing+visualization. This being said with giga interface, it might be different. Have you done some benchmarks to highlight where to find bottlenecks ?
Thanks for the great tutorial
4 Sunday, 21 December 2008 21:13
Fedir
Hello, Fulup,
I would like to thank You for the great tutorial, I'm honestly tried to follow each recommendation, reading articles on fridu.org, and watching the videos(it was very nice way to spend the weekend by the way). At this moment I could make machines, I've successfully installed Fridu-firewall and pound reverse, just there's questions about network configuration. My virtual machines couldn't get to any address to the Internet, only to internal addresses, or basic server IP.
In Your videos, when You create machines we could notice, what in Your proxmox "Cluster Node" You have internal 10.10.100.x address. In the same moment, in my proxmox installation (the same model - kimsufi from OVH), I've primary 91.x.x.x address in "Cluster node" field. Is it normal? Should I make some special cluster modifications? What is the necessary modifications to parameter 2 IP addresses with proxmox(1 primary and 1 fail-over)?
Thank You very much,
Fedir.
===== Fulup Anwser =======
The only thing that could prevent your guest to initiate request to internet, is an error on your zone configuration, or a DNS issue.
-> Internet-to-guest uses: NIC=eth0 + EXT=xxxx where xxx should be one of your public IP and eth0 your real internet NIC.
-> Guest-to-internet uses: BR=vnet0[should be OpenVZ virtual interface] INT=xx.xx.xx.0 MASK=255.255.255.0[network mask for zone's guest(s), not the IP address !!!]
-> DNS is handle by DnsMasq and my sample should work for you. WARNING: you must nevertheless make sure that guests /etc/resolv.conf point onto the right NameServer. If dns is running in your Hypervisor like in my config, your guest nameserver in /etc/resolv.conf should point onto your main PUBLIC-IP, if your DNS MASK is in a guest, then you should point on that given guest.
** If NIC|EXT is wrong port forward wont work, and you will not access your guest from Internet as defined in CreateApp
** if BR|INT|MASK is wrong your guest will not access internet (or will do it with a wrong public IP)
Note: 91.x.x.x is not a private and should not be use for guest IP, this behing said it will not prevent your config from working :)
Master tutorial
3 Saturday, 22 November 2008 03:31
Trevor-Williams
I have been waiting for this type of setup for a very long time and finally it's here. Thanks. the power of opensource. I tried the firewall setup stock, however. I have not access to the VM's nor the hypervisor coming in from the outside. Which section in the firewall will allow such access to the VMs from the internet. 

Fulup answer: the firewall as now a full dedicated page [here] which opefully should help.This being said, for incommong data stream typical error is either a wrong Zone, or a wrong AppCreate [often a simple a upper/lowercase syntax error in Label]. The best way is to tcpdump moving from your external NIC interface, to vnet hypervisor interface to close on VMs  vnet0. If it still not working please send me your config.

Whoa!
2 Friday, 10 October 2008 10:46
Felix
Hey Fulup!

Sounds like you have too much time on your hands :-) :-)
Seriously, this is really exciting stuff. I've just skimmed over your article, will probably look at your action film one of these evenings.
The "no console" limitation sounds a bit scary. I guess that will probably be added pretty quickly.
Whilst there are many advantages/disadvantages of using a full VM/zones approach, I am wondering whether there will be a future hybrid solution where we may have very tiny VMs that implement a completely isolated network stack, and then attach those to zones. Or whether there is a hybrid approach that will be integrated in zone technology - this would allow you the best of both worlds.

------------------------- Fulup element of respond to Felix ------------------------------
*** Bad *** I do not see the "no console" issue being addressed in the near future:( this being said the fact you can enter a VM, even if boot failed "cf: my bug/tip section" provides a working hotfix. After entering your not booted VM with "vzctl" you can launch "/etc/init/rc runlevel" manually to check what is breaking your automatic boot process.
*** Good *** For hybrid light/heavy containers this is already working :) For my personal hosting usage Linux is more than enough, explaining why I do not leverage hybrid containers. OpenVZ zones works smoothly with KVM full virtualization, this allow you to have Linux Zones sharing a unique kernel mixed with Solaris or Windows instance that run a private kernel. In fact the cohabitation is fully integrated inside Proxmox web GUI.
------
Very nice demo/tutorial on OpenVZ
1 Wednesday, 08 October 2008 09:08
Victor
Hi Fulup,
This is a great demo/tutorial on OpenVZ, very useful.
I will definitely give it a try, but it looks like it is just the thing that I need as well.
I did not know about pound either, I have used Apache for Reverse Proxying, but sometimes not all the Apache features are required. So pound is a good option as well.

Victor

2009年9月17日星期四

HP Insight Software HP Insight Foundation

HP Insight Software HP Insight Foundation

Managing the growing number of servers can be complex and expensive for your organization. IT managers need to address changing business needs with tools that meet the challenges of managing today's complex Datacenters.
HP provides management solutions that are designed to simplify a server's installation, configuration and maintenance throughout the entire server lifecycle. This provides the customer with higher levels of operational efficiency and highly reliable systems: www.hp.com/go/foundation.

The foundation pack includes:

  • HP SmartStart
  • HP Management
  • HP ProLiant Firmware Maintenance

SmartStart version supported (minimum): SmartStart 8.20.
http://www.hp.com/servers/smartstart

NOTE: In an effort to support reducing our environmental impact, the HP ProLiant Essentials Foundation Pack media will be available as a selectable option for this server at time of order of a CTO SKU. This will allow customers to order the number of media kits that best meet their needs and eliminate receiving unnecessary duplicate media.

ProLiant Onboard Administrator

HP ProLiant Onboard Administrator (powered by the HP Integrated Lights-Out 2 management processor) simplifies server setup, health monitoring, power and thermal control, and lights-out remote administration of ProLiant ML, DL, and BL servers. HP ProLiant Onboard Administrator functions without additional software, and can be accessed from any location via a web browser. It works hand-in-hand with HP Systems Insight Manager, Insight Control suites, and the Insight Dynamics-VSE suite helping customers unlock the value of the ProLiant platform and deliver the highest possible quality of IT service to the business. See www.hp.com/go/ProLiantOA

HP Insight Control suites

HP Insight Control suites, as product options, deliver essential infrastructure management that can help save time and money by making it easy to deploy, monitor, remote control, and optimize your IT infrastructure through a single, simple management console. Insight Control suites install and license software modules that are integrated into HP System Insight Manager.

Two Insight Control suites are available, to serve environments requiring either Linux-based or Windows-based management consoles: HP Insight Control suite for Linux, and HP Insight Control suite. See www.hp.com/go/insightcontrol

HP Insight Control suites include one year of 24 x 7 HP Software Technical Support and Update Service ensuring rapid access to HP support staff and proactive delivery of software updates. For more information about this service, please visit: http://www.hp.com/services/insight.

HP Insight Dynamics The HP Insight Dynamics for ProLiant, a product option, is an integrated command center that enables you to continuously analyze and optimize your adaptive infrastructure. This advanced infrastructure management software that allows you to analyze and optimize your adaptive infrastructure to manage physical and virtual resources in the same way. HP Insight Dynamics - VSE gives you a powerful toolkit to accelerate complex technology projects and simplify daily operations. It enables you to plan capacity and power continuously, balance across physical and virtual resources, ensure cost-effective high availability and provision infrastructure consistently.

HP Insight Orchestration, an optional extension to Insight Dynamics, enables IT organizations to provision infrastructure consistently and automatically from pools of shared resources using a self-service portal. Resources provisioned can range from a single virtual machine to complex multi-tier environments and their associated physical and virtual resource requirements.

HP Insight Recovery, also an optional extension for Insight Dynamics - VSE, enables cost-effective disaster recovery for physical and virtual environments. Application environments can be reactivated in minutes with the touch of a button to a remote location

NOTE: For more information, visit:
http://www.hp.com/go/insightdynamics
, http://www.hp.com/go/insightorchestration, http://www.hp.com/go/insightrecovery

2009年9月11日星期五

秋季养生勿盲从民谚 患胃肠道疾病忌“秋冻”

秋季养生勿盲从民谚 患胃肠道疾病忌“秋冻”

(中国)东方网   (2009-09-10)

早报导读

  (联合早报网讯)北京的金秋可以说是一年中最舒服的时节,没有夏季的湿热、冬季的寒冷,有的是早晚的凉爽和白天的碧空艳阳,让人心情开阔、睡眠充足。

  夏秋交替,免不了会让人们感受到一些不适应。身体经历一夏天的湿热积累了湿浊、毒素,使人抵抗力下降;接踵而至的冷空气,使一些胃肠道 疾病、呼吸道疾病和心脑血管疾病高发……为了安度秋季、以健康的身体迎接冬天,使人们对秋季的养生十分关注,因此也留下不少民谚、民俗,比如“春捂秋 冻”、“贴秋膘”、“秋季养肺,要以肺补肺”、“秋冬养阴,要滋阴”等。

  殊不知,这些俗理儿都要因人而异,切不可照搬照套。

  心脑血管篇

  不宜民谚:贴秋膘

  专家解读:贴秋膘是中国民间的一个传统,认为夏季之后,人们应该多吃肉类,增加营养、储备脂肪,以备过冬御寒。但是这个传统适用于过去 以谷类为主的单一、匮乏的食物条件,现在生活中食物种类多,人们摄入的脂肪、蛋白质含量并不低,没有“贴秋膘”的必要了。而且,对于心脑血管患者来说,更 不宜“贴秋膘”,导致疾病发作。

  心脑血管疾病患者秋季锻炼宜选晚饭后

  随着秋季的来临,心脑血管病患者进入发病的高峰季节。据调查统计显示:秋冬季节脑血栓、冠心病的发病人群占全年发病人群的比例高达69.5%。

  首都医科大学附属北京中医医院心脑血管科主任医师刘红旭说:“秋季早晚寒凉,变冷的空气容易导致血管收缩,威胁心脑血管疾病患者的健康。因此,心脑血管患者秋季不宜晨练。”

  秋季的气候特点是温差变化较大,冷暖不定。长期高血压、动脉粥样硬化患者和脑血栓、脑梗塞、冠心病患者遇到冷空气刺激时,因生理反应使 血管骤然收缩,由于血管的内壁较厚,管腔狭窄,加之有大量的脂类沉积与硬化斑块,导致血液流通受阻,从而极易引起心脑血管疾病的发作和复发。

  刘红旭建议,老年人和心脑血管患者锻炼最好在晚餐之后,如果是上午活动,也尽量晚一些,以减少心脑血管发病风险。

  呼吸道疾病篇

  不宜民俗:秋季养肺,要以肺补肺

  专家解读:中医确实有取类比象的养生理论,认为可以通过“以形补形”的方法来改善原有病灶或是预防相对应器官的发病。秋季气候干燥,呼 吸系统疾病多发,养肺就成为人们“想当然”的做法。其实,健康的人没有必要针对肺这个脏器进行饮食或药物调补,从生活的日常起居多注意一些就可以了。

  适应环境,预防呼吸道疾病

  入秋时气温下降较快,遇到冷空气时,人体鼻咽部黏膜上的血管扩张,黏膜充血,具有保卫作用的绒毛运动迟缓,从而降低了黏膜的抵抗力。此时细菌、病毒便可乘虚而入,引起呼吸系统疾病。常见的有流感等,比较严重的可能患上咽喉炎、肺炎等。

  秋季感冒多为“伤风”,是一种常见的呼吸道疾病,早期症状有咽喉疼痛灼痒、鼻塞、打喷嚏、流鼻涕,少数会出现低热、头痛等症状。人们应该根据天气冷暖变化适时增加衣服,避免风寒侵袭;并通过适当锻炼、保持充足的睡眠时间来提高机体的免疫机能。

  支气管哮喘等过敏性疾病除了要远离致病原之外,还要注意保持空气湿润。慢性呼吸道疾病患者的居室要多开窗通风,加快空气流通,保持空气新鲜。室内湿度的调节则可通过晾湿毛巾和衣物来提高湿度,有条件的话,可以使用加湿器,控制室内湿度的恒定。

  胃肠道疾病篇

  不宜民谚:春捂秋冻

  专家解读:“春捂秋冻”最早是源于我国古代人们的穿衣习惯,夏季到冬季之间可过渡的衣服很少,往往是脱掉夏装就直接穿棉,或脱掉棉衣直 接穿夏装,因此留下了“春捂秋冻,不得病”的古谚。“秋冻”可保证机体从夏热顺利过渡到秋凉,提高人体对气候变化的适应性与抗寒能力。但盲目推崇“秋冻” 则会危害健康,引发胃肠道疾病。

  老胃病加重,肠胃炎高发

  秋季是胃病的多发与复发季节,受到冷空气刺激后胃酸分泌增加,胃肠发生痉挛性收缩,抵抗力和适应性随之降低。而且,秋季多数人情绪易烦 躁,加上过度劳累,如果防护不当,就会引发胃肠道疾病而出现反酸、腹胀、腹泻、腹痛等症状,或者使原来的老胃病加重,严重者还会引起胃出血等并发症。

  秋季也是急性肠胃炎发病率较高的季节。秋季水果蔬菜大量上市,一些人又有秋季进补的习惯,饮食比较杂乱,如螃蟹、鱼、虾、苹果、梨、红枣、柿子等,很容易引发肠胃病。特别是老年人生理退化,肠胃的运动、吸收功能减退,抵抗力下降,更容易患急性肠胃炎等消化系统疾病。

  保养肠胃,别忽视保持乐观情绪

  首先,应特别注意胃部的保暖,防止腹部受凉,患有慢性胃炎的人须尤其小心腹部的保暖,适时增加衣服,夜间睡眠时要盖好被褥,以防止腹部着凉而引发或加重胃病。

  其次,要调节饮食,可以多吃些滋阴润燥的食物,避免燥邪伤害,少吃辛辣,防止其侵蚀胃黏膜和溃疡面而加重病情。有老胃病的人或者肠胃一 直不太好的人应做到少食多餐,定时定量,同时注意进食时细嚼慢咽,以利于消化吸收,减轻胃肠负担。另外,秋季气候干燥,容易导致便秘,应该多吃水果补充水 分。

  同时,心理健康对肠胃也很重要。肠胃道疾病的发生与发展,与人的情绪密切相关。因此,保持精神愉快和情绪稳定很重要,避免焦虑、恐惧、紧张、忧伤等不良情绪的刺激。

  来源: 中国新闻网

2009年9月4日星期五

Keep your RSS feeds simple with Arr! SS

Keep your RSS feeds simple with Arr! SS

Posted by Joe on September 3, 2009

One way I frequently use my BlackBerry is to catch up on reading. It's not the best layout for doing so, but once you get used to reading in screen-sized blocks, it's actually pretty convenient. To that end, Cooper reviewed a ton of BlackBerry RSS readers. And, of course, there's always the BBGeeks Viigo reader. Yet many of these readers, including the popular Viigo and Google Reader Mobile, are pretty resource intensive. Adam at CrackBerry points us to a much simpler one: Arr! SS. It's no frills, loading just the text from your feeds. In other words, it's great for keeping up with your reading while keeping memory use in check.

Infinityball will offer two versions of this application: free and paid. Both versions are rather similar right now, so I suggest you download the free version and give it a whirl. That way you'll have a better idea of whether you'd like to drop $1.99 on the paid version.
What will be different about the paid version? Google Reader integration for one, with the ability to sync individual items and entire feeds (so if you delete a feed in GR, it will also delete in Arr! SS and vice versa). They also claim the premium version will be faster, though it's tough to get faster than it is right now.

Also planned for future premium releases: podcast support, RSS guide, OPML import/export, background notifications, and an integration with your Messages application. The last one is pretty intriguing. I might go for select feeds delivered to my inbox.

If you want to jump right into the premium version, you can get Arr! SS at the BBGeeks Store for $1.99 until September 30. We'll see if that sale lasts a little longer if they take their time upgrading the premium features.

Kernel 2.6.31 to speed up Linux desktop

Kernel 2.6.31 to speed up Linux desktop
X desktop responsiveness doubled under high memory
Rodney Gedda  04 September, 2009 10:32

With the next version of the Linux kernel, 2.6.31, due for release soon, Linux desktop users can look forward to a faster experience in addition to USB 3.0 support and new Firewire drivers.

The kernel developers have been working on improvements to desktop interactivity, particularly when it's under memory pressure since the last release, version 2.6.30, in June.

Desktop applications can experience long and noticeable pauses when the application's code path jumps to a part of the code that is not cached in memory and needs to be read from the disk, which is slower.

However, recent kernel memory management scalability work can result in a desktop environment with poor interactivity as applications become unresponsive too easily.

In version 2.6.31, some heuristics have been used to make it much harder to move the "mapped executable pages" out of the list of active pages, according to Kernelnewbies.org.

"The result is an improved desktop experience; benchmarks on memory tight desktops show clock time and major faults reduced by 50 per cent, and pswpin numbers (memory reads from disk) are reduced to about one-third. That means X desktop responsiveness is doubled under high memory pressure."

Furthermore, memory flushing benchmarks in a file server shows the number of major faults going from 50 to 3 during 10 per cent cache hot reads.

Linux foundner Linus Torvalds, first developed the operating system for his desktop and it rose to promince as a commodity Unix server.

However, adoption of Linux on PCs and notebooks has remained niche compared with Windows and only became more of a mainstream alternative in recent years.

Estimates vary wildly as to how many Linux desktops are in use today, but according to market share data from Net Applications, the proportion of Linux desktops peaked at 1.17 per cent in May 2009 and has since dropped to 0.94 per cent in August.

The advent of Windows 7 in October may drive Linux's desktop market share down even futher.

It's not all doom and gloom for the penguin, however, as the improvement in kernel memory management, X.org display server developments, graphics driver updates and advancements in the two main desktop environments – GNOME and KDE – all continue to enhance the Linux desktop ecosystem.

Another improvement coming with 2.6.31 is kernel mode-setting support for ATI Radeon graphics cards.

Kernel mode-setting moves graphics mode initialisation from the X server startup process to the kernel, enabling faster user switching and a more seamless startup experience.

Peripheral developments that will also improve the Linux desktop experience include support for the new USB 3.0 specification and a new Firewire stack.

Intel has been working USB 3.0 device support for hardware that implements the eXtensible Host Controller Interface (xHCI) 0.95 specification.

USB 3.0, or SuperSpeed USB, ups the theoritcal maximum data transfer rate to 4Gbps.

No xHCI hardware is available yet, but the kernel drivers have been tested under the Fresco Logic host controller prototype.

For Firewire, 2.6.31 brings improved support of fine-grained access permission policies for application programs in userspace, IP networking with the new driver stack, and support for Firewire disks larger than 2TB.

"No longer marked as 'experimental' in the kernel configuration menu, distributors who provided the older ieee1394 driver stack so far are encouraged to build and install both driver stacks," according to the project.

The last release candidate of the new Linux kernel was 2.6.31-rc8 on August 28.

2009年9月3日星期四

Comparing windows and Linux hardware management.

Comparing windows and Linux hardware management.

Locutus (System Administrator) posted 9/2/2009 | Comments (4)
An operating systems most basic function is to act as a layer between the computer hardware and the user space programs. User space meaning the programs you use as a computer user, ie. office, email, internet and games programs. What an operating system provides to those user space programs is a standard interface to the computers hardware, no matter what type of hardware that is.

For example, to see all those pretty pictures on the screen in front of you the program you are currently using must send that data to the graphics card, which is then displayed on the screen. Yet there are umpteen thousands of different makes and models of graphic cards. In the days before proper operating systems each program had to interact directly with the hardware. This means that if you change the hardware you needed to change the program to match.

With the advent of operating systems acting as a layer (Mmmm layer cake :) between the hardware and programs this difficulty for the programmers was removed. The program you are currently using just sends the data to a specified operating system interface, which never changes. The operating system, then spits that information out of a different interface. The specially written hardware drivers then translate that information to match specific hardware. The reason for the layer between driver and program is to enable the drivers to be easily changed and updated without disturbing the rest of the system.

With both windows and Linux the theoretical method is the same. The difference lies is how they are approached practicably. As I said before there are many different makes and models of the same type of hardware. As an example I will use graphics cards. Each model of graphic card has a set of chips (minus the fish) called a chipset. Different manufacturers use this chipset to produce their own make of graphic cards.

In the windows world each manufacturer produces a specific driver for their own make of cards. Windows does not take the responsibility of providing drivers for hardware. When the hardware is installed so is the driver to run it. If you change the graphics card to a different make, even if it is the same model then you cannot use the existing driver. You need to install the matching driver for that make of card. In short windows driver support is manufacturer specific.

In Waynes Linux's world it is a completely different story. Almost all driver support is supplied by the Linux kernel in the form of modules which can be added, changed and removed at will. As I specified earlier each different make of a particular model of graphics card uses the same chipset. When the hardware is installed the relevant driver for the chipset of that particular graphics card is activated and it can be used. If you change that graphics card to a different make, even if it is the same model. The same driver is used. You do not need to install a different driver. In short Linux driver support is chipset specific.

What this means is that with windows being manufacturer specific every different piece of hardware needs to have a new driver installed. With Linux being chipset specific only different chipsets need to use different drivers. This is why Linux advocates state that Linux supports more hardware out of the box than what windows does. It also makes for a more stable and easy to maintain system.

加斯帕尔·诺埃:一人反对一切


Sent to you by monokeroz via Google Reader:


via Déjà-vu by 大旗虎皮 on 9/3/09

1963年12月27日,加斯帕尔·诺埃(Gaspar Noé)生于阿根廷布宜诺斯艾利斯,他爸爸路易·菲利普·诺埃(Luis Felipe Noé)是超现实主义画家。六岁时,库布里克的《2001太空漫游》打开了这个阿根廷男孩看待世界的内心之眼。十二岁,诺埃跟随父母移民法国,这场命中注定的"迁徙"让加斯帕尔·诺埃永远获得了批判的武器:电影。拉丁文化有着本能、直觉、充满想象和浓郁的活力,但不同的世界把拉丁文化塑造成不同的电影。如果墨西哥导演在好莱坞变成制作"电影玩具"的好手,那这个阿根廷人则因登陆欧洲而蜕变为人神共怒的"电影恶魔"。

五年后,诺埃成为卢米埃尔高等电影学院最年轻的外裔学生,时年17岁。两年后,他带着卢米埃尔学院的电影高等技术文凭冲上了战场,带着他本能的、直觉的、充满想象和浓郁活力的性格,以及一个密不透风、癫狂、尖锐的影像世界向现代社会发起了进攻。

毕业三年,这个愤世嫉俗的年轻人向社会发射了第一枚子弹:实验短片《月夜》(Tintarella Di Luna)立足创新,劲道十足。短片用35毫米黑白胶片完成,呈现了一个前所未有的封闭、幽暗和压抑的末日般的世界。加斯帕尔·诺埃在构图、摄影上的尖锐和精致,以及与对道德的绝对蔑视,让人想起了实验时期的"电影兰波"菲利普·加莱尔(Pilippe Garrel)。影片是法国运河电视台(Canal Plus)购买最早的短片之一,之后购买的就是大卫·林奇的《橡皮头》。又过了两年,短片《苦涩的脊髓》(Pulpe amère)延续着耳目一新、但难以下咽的尖锐风格,讲一个压抑的中年男人试图在房间中强奸一个少女的幻想故事。不难看出,该片已初具《马肉》和《我企硬》的雏形。

短片时期,加斯帕尔·诺埃为流放巴黎的阿根廷导演费尔南多·索拉纳斯(Fernando E. Solanas)做助理导演,同时修习哲学课程。他似乎觉得新锐的视听效果还不够犀利,不能把他的电影打磨得更加锋利,所以才选择求助于形而上学。

加斯帕尔·诺埃的发展步调印证一个标准的电影天才的成长形态:迅速,极端,迫不及待,又不可一世。界定天才的标准最接近于怪胎,从行为和能力上把天才从普通人里化简出来到最后一步,就是区别天才和怪胎,但在历史上那些天才面前,这一步显得缺乏必要性。如果加斯帕尔·诺埃的经历证实了天才的诞生(17岁考入卢米埃尔学院已经是卓尔不群的天才了),那他的作品就是法国当代电影中横空出世的令人毛骨悚然、望而生畏的怪胎。他妈妈甚至因他性格乖僻而带她看过心理医生。医生问:你喜欢看恐怖电影吗?喜欢。医生诊断此人逻辑敏锐,精神正常。

在诺埃的成长中,库布里克的《2001太空漫游》有着难以企及的地位。人们问他:你从什么时候想拍电影的?从"2001";你认为哪部片子位居其它影片之上?"2001"。对库布里克的酷爱塑造了加斯帕尔·诺埃的艺术嗜好:"我总希望把我与法国电影那些习惯人群区别开!"与FEMIS学生偏向文艺青年的委婉叙述相比,卢米埃尔学院则扩散着显影药水一般刺鼻的技术实验气息。他们瞧不起"叙述",无视"言说",他们不仅强调"做",而且追求"做的效果",电影必须在视觉、风格和价值批判上追求"第一效果"。

1987年,加斯帕尔·诺埃夹着40分钟长度的电影炸弹《马肉》(Carne)进驻了戛纳电影节,拉开了他对社会宣战的序曲。《马肉》开始就是血淋淋的杀马镜头,诺埃采用了后来成为主流电影时髦的"主人公冷叙述法"(《天使爱美丽》的开场叙述),讲述一个马肉店小老板、一个面无表情、缺乏情调、内心封闭的屠夫,日复一日、年复一年过着枯燥生活。面对女儿越来越成熟的肉体他产生了无以自拔的欲望,最终他误以为女儿被人强奸而把屠刀插进了那个家伙的嘴巴。影片弥漫着压抑、干燥、冷冽的气息,画面始终弥漫着血污一样的红,一种暴雨过后阴沟翻滚的腐朽气息,一副肆无忌惮的颓废和末世色彩。奇怪的机位(经常切掉人的眼睛)、僵直的动作,影片除了少量从广播里传出的音乐,令人印象最深的就是不断出现的沉重顿音,让人害怕和不安。

《马肉》在视听语言和社会批判上的直接性令人猝不及防、目瞪口呆。影片开始就明目张胆地写出"本片会让青少年观众产生严重的心理不适"等字样,这类对那些已走进电影院、坐在椅子上的观众毫无意义的警示,在他后来的电影作品不断出现,成为他独一无二的标签。他在电影中直接与观众对话,在《我企硬》结尾的暴力幻想戏之前,诺埃以数秒倒计时的方式请某些保守派观众提前离场。看这样一部电影,你不但会被导演的勇气感到不寒而栗,也会感到他就像一个玩世不恭、心思缜密的流氓,带着冷嘲热讽的表情从人性的最底层猛烈强暴这个世界,甚至还有几分幽默感。在西文中,"玩世不恭"与"犬儒主义"是一个词,它代表一种态度,而我们则经常把这两个词分开用,在中国似乎只有王朔身上高度集中了这两个词的共同含义,玩世不恭地一个都不放过。

《马肉》获得了戛纳电影节国际影评人周奖,很多人劝诺埃拍一部《马肉》的加长版,于是他用了7年时间拍摄了《马肉》的续篇《我企硬》,走向了偏执狂的极限。1985年,他让他的爸爸在自己的短片里演了精神变态杀手,1997年,他自己在好友让·古南(Jan Kounen)的《太保密码》中客串一个卖土耳其烤肉的混混。诺埃与让·古南出现在一起并不奇怪,他们都是电影偏执狂,都对世界毫不让步,都疯狂尝试致幻剂,都拍摄出令人惊心动魄的画面。

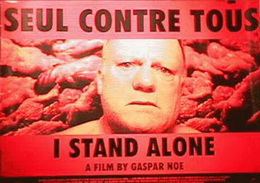
用"我企硬"这个词翻译Seul contre Tous不太文雅,影片直译过来是"一人反对一切",虽然这样翻译能准确传达影片誓死不降的态度,但丧失了那种粗俗、污浊和激进的乖张反常。

影片是《马肉》的续篇,屠夫伤人后被判入狱,不得不卖掉马肉店担保提前释放,而女人被关进收容所。他与肥胖的咖啡馆女主人离开巴黎,准备到里尔东山再起。但一切都是骗局,这不是一个献给穷人的世界,此时是1980年,法国大选在即,社会的萧条历历在目。屠夫在忍无可忍中痛扁胖女人,带着枪走上因身无分文、无路可走而濒临暴力"革命"的不归路。

《我企硬》要比《马肉》极端十倍,依然是污浊的红色和仿佛病态心脏猛烈颤动的顿音,影片像一把锋利的刀子,割开艺术观赏活动的虚伪表皮,寒冷、坚硬的叙述,主人公板砖一样的毫无表情的面孔,影片伴随着主人公不断加快的诅咒式旁白,跟随人物逐渐走入濒临崩溃的世界。诅咒自己的亲身骨肉,唾弃垂死的老人,歧视外国人,谩骂同性恋,仇视富人,最终在幻想中与女儿同归于尽。

从某种角度看,《我企硬》像布莱松《扒手》的先锋实验版,人物表面行动上的冷与罪人袒露内心世界的热,但《我企硬》拒绝赎罪,影片最后屠夫杀死女儿的极端暴力场面,因进行了1%的让步而成为主人公的瞬间幻想,但结局依然是灰暗的,他陷入对女儿的性幻想中无法自拔。加斯帕尔·诺埃不是布莱松,更不是布莱松的追随者。布莱松是电影社会学家,他追求行为的精确性去挖掘动机的清晰度,诺埃的人物是一条被世界逼上绝路的恶犬,他时刻准备攻击我们。《我企硬》几乎是一则反社会的宣言,一部精神无政府主义的内心史诗,就像影片开场的那段流氓哲学:什么是道德?道德就是有钱人的道德;什么是正义,谁有枪谁就是绝对的正义。影片以这种共同毁灭的方式与公众的道德和观赏习惯剧烈地正面对撞。

这就是诺埃的电影锋芒,它锐利,干脆,自信十足,狂妄至极。影片不断传来主人公的内心独白,在这个肮脏、猥琐男人的内心世界,对自私、欲望、堕落、仇恨、道德、不公、背叛等等一切污秽毫不留情地批判,甚至是直接谩骂。

"批判艺术"可有两个层次:社会学意义的和超社会学意义的批判,前者针对某个具体国家、历史和社会的事实和秩序,它有非常明确的攻击目标和现世诉求而,因而必须确立放大具体的话语背景以强化打击效果,而超社会学意义的批判则放弃具体语境的确立,它直接针对人与人之间结构性的堕落,以及这种堕落结构导致的整个世界的罪恶秩序。显然,批判如果想达到后者的批判幅度和深度,必须是富有野心的,具备真正的洞察力和饱和的激情。加斯帕尔·诺埃正努力靠近后者,而且从开始到现在毫不妥协。

2002年,加斯帕尔·诺埃用惊世骇俗的《不可撤销》以高空俯冲的方式在世界电影界强行着陆。关于这部影片,那些热爱追随电影动态的人已耳熟能详了,影片以绝对意义的语言和叙述表达了命运之不可撤销。影片用灭火器砸碎脑壳和地下道强奸确实让人产生强烈的生理不适,兼具生理性的恐怖(horror)和心理性的恐惧(terror)。摄影机不同转动,从快到慢,从模糊到清晰,从暴力悲剧到充满幽默对白的生活喜剧,诺埃试图让人明白,叙述方向的变化(先讲悲剧结局后讲喜剧开始)无法改变悲剧本身。以假乱真的电影特技在诺埃手里不是用来蒸腾观众快乐哲学的催化剂,而是展开道德批判、社会批判的恐怖的手术刀。

《不可撤销》在法国掀起了轰动性的争议,有人认为那场带有模糊色情色彩的强暴戏和结尾时蓝天绿草上的伊甸园场景,本质上都是"可笑而蛊惑人心的旁白"(mêmes dérisoires apartés démagogiques),是商业觊觎下的虚伪做作。勒内·普雷达尔否认加斯帕尔·诺埃这种过分激进和极端先锋,认为他不过是一个笨拙的库布里克、柯南伯格、祖劳斯基及马丁·斯科西斯的抄袭者,但他并没有获得这些前辈的真传,反而陷入极端形式革命的漩涡。我承认诺埃在可能的意义上确实是柯南伯格、祖劳斯基的后继者,但他并非是简单的愤青抄袭家。但是,是什么原因让加斯帕尔·诺埃的呐喊和愤怒招来非议呢?他与他的前辈说的东西是相同的,只不过说的方式不同罢了。戈达尔除了不用下作画面刺激观众之外,与诺埃探讨的议题是一致的,只不过戈达尔把枪口直接对准了政治和财富阶级,而加斯帕尔·诺埃则是"一个人反对一切"。

真正的问题在于,对法国这个优雅的老牌发达国家,如此激进的愤怒已显得不合时宜,人们生活稳定,现实中没有那么可以支撑愤怒的内容,人的内心异常平静。或许诺埃只是提供一个愤怒的容器,让观众向里面倾倒适合的内容,所以,他的电影或许在今日中国纷乱的现实中会比法国产生更多共鸣。

克尔凯郭尔曾说,在剧院中,观众和听者才是演员,他其实是在上帝面前表演。这用在加斯帕尔·诺埃的电影上最意味深长了。

加斯帕尔·诺埃电影年表

  • 1985,《月夜》(Tintarella Di Luna),短片,18分钟
  • 1987,《苦涩的脊髓》(Pulpe amère),短片,6分钟
  • 1991,《马肉》(Carne),中片,40分钟
  • 1998,《我企硬》(Seul contre tous,又译:一人反对一切,独自站立)
  • 2002,《不可撤销》(Irréversible)
  • 2006,《性爱禁区》(Destricted),其中的短片《我们独自做爱》(We Fuke Alone)
  • 2009,《遁入虚无》(Soudain le vide)
标签:


Things you can do from here:


在哀榮和冷清之間

在哀榮和冷清之間


在哀榮和冷清之間

◎ 傅國湧     


九十八歲的季羨林和九十三歲的任繼愈同日去世,尤其是季羨林的離世引起了廣泛的關注。他們的遺體覆蓋著鮮紅的黨旗, 綴擁在一片鮮花之中,黨國要人或送花圈,或戴白花,官方媒體以鋪天蓋地的好詞好句為他們送行,可謂備極哀榮。在這片依然在強權的鐵索主宰之下的土地之上, 在這個充滿謊言、諂媚和奴顏的時代裡,兩個老人的葬禮和所有的哀榮,為一切依附於權力、臣服在權力腳下的知識份子提供了又一個範例,只要與權力保持這樣一 種良好關係,為「盛世」唱唱讚歌,或者至少與「盛世」保持合作,不僅生前可以享有榮華富貴,死後同樣可以得到巨大的風光體面。對於缺乏超越性追求的國人來 說,許多人往往過不了這一關。


知識份子的公德高於私德


  我無意苛責這兩位謝世的老人,畢竟他們在各自的專業上都是有貢獻的,何況他們之間也很難一鍋煮。相比之下,任繼 愈先生主要是學問中人,少問世事,低調為人,生前沒有在公眾視線中頻頻出現,也沒有拋出什麼引起非議的觀點,至少在私德上是無虧的。關於季羨林先生,廣為 流傳的那個故事說他曾在路上為北大學生看行李,就算真的,其實也只是老人的私德。中華民族向來不缺對個人私德的要求,也不缺在私德上站得住的人,缺的是懷 抱公德心,為民族正氣、為文明進步孜孜努力的人。梁啟超先生一百多年前率先引入的「公德」這個維度,正是通往一個健康公民社會不可或缺的前提條件之一。現 代社會在評價一個知識份子時,應更多地使用公德的尺度。


  兩位老人身後的哀榮,使我想起另一位北大老人,九十八歲的倫理學家周輔成先生,他在今年五月二十二日謝世後的冷 清和寂寞,舉國媒體的沉默,評論家們的缺席,我只在北大哲學系的網站上看到一則訃告。原因何在?當然不是周輔成先生的學術成就不夠,作為中國倫理學這個學 科的重要奠基人,人性論和人道主義的宣導者,北大哲學系的資深教授,他在專業上同樣有出色的貢獻,他在上世紀六、七十年代主持編譯的《西方倫理學原著選 編》、《從文藝復興到十九世紀西方政治家思想家哲學家有關人性論人道主義言論選輯》,給國人提供了十分珍貴的精神資源和思想火種,受惠的不僅是那些專業研 究者。


周輔成教授葬禮一片冷清


  就因為他追求浩然獨立的人格,就因為他的良知常常悖逆官方的意志,他成了官方不喜歡的人,很少在媒體露面,從而 被這個蠅營狗苟的所謂主流社會刻意遺忘了。周先生的關門弟子、清華大學哲學系教授萬俊人曾在電話中向四川的蕭雪慧老師感歎:葬禮太簡陋了。周先生當然不會 在意葬禮的冷清,更不會把官方的獎賞當作寶貝,他有自己的價值尺度,有自己的評判標準。生前的榮譽、鮮花和掌聲他尚且毫不在乎,何況身後。


  說到底,真正值得舉世尊敬的是周輔成先生,因為他保持了中國知識份子最可貴的品質,不僅是私德上的無瑕疵,更重 要的是他身上體現出來的公德心,他向一個殺害無辜的強權說不,他為一個現代中國仗義執言,他為那些有理想、有才華的學生、後學的不幸遭遇而憂心。他是一個 有真性情的人,一個堅守道義立場的人。上世紀八十年代初,當他的學生胡平因參與區人大代表直選,並以力倡言論自由被北大選民選上之後,卻遭報復,畢業後找 不到工作,他以七十多歲高齡乘公共汽車在北京城裡四處奔走,為學生聯繫單位。因此招來有關部門這樣一句話:「胡平自由化,他的老師比他還自由化!」西南民 族學院的蕭雪慧老師因捲入八九年的民主浪潮而身陷囹圄,一九九一年出獄不久,她竟意外地收到了周先生的明信片,她為此而深感溫暖,此前他們之間並無交往。 蕭老師告訴我,長期以來,周先生對她一直關心有加,為她的遭遇深為不平。


  一九九六年十二月,周輔成先生在其著作《論人和人的解放》後記中寫下:「知識是可貴的,道德是可貴的,文化也是 可貴的。這些都是人民艱苦奮鬥、用血汗換來的成績。切不可算在名利熏心的『英雄豪傑』們的帳上......我佩服古往今來站在人民一邊,捍衛人民的權利與 人格的有良心的志士們的氣節與靈魂。我手中只有半枝白粉筆和一枝破筆,但還想用它來回應這些古今中外賢哲們的智慧和勇敢,向他們致敬。」他自己同樣保持了 這樣的氣節和靈魂,可以毫無愧色地進入古今中外賢哲的行列中。在北大朗潤園他家的牆上,有一張他親手書寫的條幅:


  「居天下之廣居,立天下之正位,行天下之大道,得志與民由之,不得志獨行其道。富貴不能淫,貧賤不能移,威武不 能屈。此之謂大丈夫。」--他以孟子的這番話自勵,實際上,他不僅做到了孟子所謂的大丈夫,而且是一個現代意義上的知識份子,在一個不義的強權面前,他始 終沒有低下高貴的頭顱,保持著獨立的批判,努力發出不苟合的聲音。


六四後保持知識份子氣節


  如果說二十年前的那個春天,呼籲民主是當時的風氣,周輔成先生在要求釋放魏京生等良心犯的公開信上簽名沒有多大 的風險。那麼,在一九九五年,經過血腥的「六四」大殺戮之後,多少人被淋漓的鮮血嚇破了膽,在知識界盛行犬儒主義,人們紛紛選擇明哲保身的大趨勢下,他在 許良英先生起草的〈迎接聯合國寬容年,呼喚實現國內寬容〉公開信上簽名,就需要足夠的道義勇氣,在這份公開信簽名的人包括王淦昌、樓適夷、楊憲益、吳祖光 等在各領域有影響的知識份子,曾引起強烈的反響,也讓殺人者大為吃驚,當時離「六四」不過六年。如果放在歷史的天平上,不是以現實利益的得失來權衡的話, 他們在一個人權缺乏保障的時代,為每一個個體生命的人權大聲吶喊,為一個古老民族的文明進步而承擔自己的責任,不僅大大彰顯了人格的力量,而且呈現了中國 知識份子在公德層面的擔當意識。替學生看一次行李雖也可以成為茶餘飯後的美談,但不可與此同日而語。


  同為穿越了二十世紀無數風雲變幻的學術老人,三個人身後哀榮的巨大反差,給我們提出了這樣一個問題,在向現代社 會轉型的這個過程中,我們到底更需要什麼樣的知識份子?固然我們需要各個專業領域都能出現私德無愧的專家型知識份子,對他們的貢獻同樣要給予足夠的評價, 但是,我們更需要周輔成先生這樣的知識份子,不光在專業上有卓越的建樹,並且熱切地關懷社會,不因為阻礙社會進步的力量掌握了現實權力而屈膝,持續地捍衛 自己的獨立選擇,一如既往地保有純潔的良心,承擔自己該承擔的一部分,哪怕為此而「因故退休」,哪怕因此而被邊緣化,被官方所冷落。


  如果一個民族,毫不吝嗇地把最高的榮譽都獻給了那些被官方認可、受官方肯定的文化人,跟在官方的屁股後面樂顛顛 的,絲毫也沒有意識到被愚弄、被導向了,完全忽略了那些真正值得我們尊敬的知識份子,那才是最大的悲哀。隨著時間的推移,我深信,最後挺立在精神史上的將 是周輔成先生這樣的民族脊梁。畢竟,官方的榮譽歸官方,歷史的榮譽歸歷史。

Linux 死机了怎么办

Linux 死机了怎么办

今天在 Linuxgem.org 上面发现一篇很有意思的文章,和大家分享。

{Via http://blog.upsuper.org.cn/what-to-do-if-linux-crash/}

Linux 会死机么?我可以很肯定地说,会!要让 Linux 死机很容易,但难的是在死机以后如何安全的让他摆脱死机状态,本文讲述如何从 Linux 的死机状态中挣脱出来。

Linux 死机有很多种情况,最常见的是系统负载过高导致的。如上次介绍的 fork 炸弹就是这个原理,此外还可以运行内存耗用极大的程序(如虚拟机),也会迅速提升系统负载。由于系统负载过高导致的卡死,一定是解决的越快越好!此时必须 记住的是,不能再试图依赖任何图形界面的东西,如 Gnome 的系统监视器(这是我从 Windows 遗留下来的愚昧习惯……),这只会继续加重这种卡死的局面。那怎么办?

不要怕,Linux 最初就是不需要图形界面的,因为有一个很强大的文字界面。按 Ctrl-Alt-F1(F1-F6 一般来说都可以),然后等一会儿,就会切换到 tty,也就是所谓的文字界面。这个时候需要用用户名密码登入。注意,可能键盘输入的速度比较慢,不过应该还是可以忍受的。下面在提示符后面输入 top 回车,这时会看到一张动态的表,上面列出了耗用资源最多的进程。观察它刷新一两次,按q退出,然后输入 kill ,其中的 PID 你可以在 top 里面看到。这个时候应该会快了不少,如果你发现没有成功结束掉,就再输入 kill -KILL ,这次基本上就没问题了。

除了上面这种情况外,一些底层软件的 bug 也可能导致一些奇怪的死机问题。我某位同学近日就因为莫名其妙的死机强制重启把 ext4 的分区给伤了。(最后是 sysreccd 修复了,貌似是分区表部分损坏)据其说,死机是键鼠均无反应。一般来说,系统负载高导致的死机,在可怕键盘也会有反应,有人说如果死机到键盘无响应"负载 都无限大了",亦有人说这可能是 X Server 与驱动配合有问题导致的。不过我们考虑一下遇到这种情况怎么办?

OK,这是今天才学到的方法,叫做 reisub,这个方法可以在各种情况下安全地重启计算机。大家在键盘上找,可以找到一个叫做"Sys Rq"的键,在台机的键盘上通常与 Prt Sc 共键,在笔记本可能在其他位置,如 Delete。以台机为例,要使用这种方法需要按住 Alt-Print(Sys Rq),然后依次按下 reisub 这几个键,按完 b 系统就会重启。

下面解释一下这个方法:其实 Sys Rq 是一种叫做系统请求的东西,按住 Alt-Print 的时候就相当于按住了 Sys Rq 键,这个时候输入的一切都会直接由 Linux 内核来处理,它可以进行许多低级操作。这个时候 reisub 中的每一个字母都是一个独立操作,他们分别表示:

unRaw 将键盘控制从 X Server 那里抢回来
tErminate 给所有进程发送 SIGTERM 信号,让他们自己解决善后
kIll 给所有进程发送 SIGKILL 信号,强制他们马上关闭
Sync 将所有数据同步至磁盘
Unmount 将所有分区挂载为只读模式
reBoot 重启

这6个字母的顺序是不可以记错的。那怎么记呢?这里提供一个个人认为比较好的方法:单词 busier(busy 的比较级,更忙)倒过来就是了。

基本上就这样了,Linux 的死机本来就不多见,现在见了也可以安全解决,多好~

2009年9月2日星期三

Network-attached storage

Network-attached storage

From Wikipedia, the free encyclopedia

Jump to: navigation, search

Network-attached storage (NAS) is file-level computer data storage connected to a computer network providing data access to heterogeneous network clients.

Contents

[hide]

[edit] Description

Visual differentiation of NAS vs. SAN use in network architecture.

A NAS unit is essentially a self-contained computer connected to a network, with the sole purpose of supplying file-based data storage services to other devices on the network. The operating system and other software on the NAS unit provide the functionality of data storage, file systems, and access to files, and the management of these functionalities. The unit is not designed to carry out general-purpose computing tasks, although it may technically be possible to run other software on it. NAS units usually do not have a keyboard or display, and are controlled and configured over the network, often by connecting a browser to their network address. The alternative to NAS storage on a network is to use a computer as a file server. In its most basic form a dedicated file server is no more than a NAS unit with keyboard and display and an operating system which, while optimised for providing storage services, can run other tasks; however, file servers are increasingly used to supply other functionality, such as supplying database services, email services, and so on.

A general-purpose operating system is not needed on a NAS device, and often minimal-functionality or stripped-down operating systems are used. For example FreeNAS, which is Free / open source NAS software designed for use on standard computer hardware, is just a version of FreeBSD with all functionality not related to data storage stripped out. NASLite is a highly optimized Linux distribution running from a floppy disk for the sole purpose of a NAS. Likewise, NexentaStor is based upon the core of the NexentaOS, a Free / open source hybrid operating system with an OpenSolaris core and a GNU user environment.

NAS systems contain one or more hard disks, often arranged into logical, redundant storage containers or RAID arrays (redundant arrays of inexpensive/independent disks). NAS removes the responsibility of file serving from other servers on the network.

NAS uses file-based protocols such as NFS (popular on UNIX systems), SMB/CIFS (Server Message Block/Common Internet File System) (used with MS Windows systems), or AFP (used with Apple Macintosh computers). NAS units rarely limit clients to a single protocol.

NAS provides both storage and filesystem. This is often contrasted with SAN (Storage Area Network), which provides only block-based storage and leaves filesystem concerns on the "client" side. SAN protocols are SCSI, Fibre Channel, iSCSI, ATA over Ethernet (AoE), or HyperSCSI.

Despite differences SAN and NAS are not exclusive and may be combined in one solution: SAN-NAS hybrid

The boundaries between NAS and SAN systems are starting to overlap, with some products making the obvious next evolution and offering both file level protocols (NAS) and block level protocols (SAN) from the same system. An example of this is Openfiler, a free software product running on Linux.

[edit] History

Network-attached storage was introduced with the early file sharing Novell's NetWare server operating system and NCP protocol in 1983. In the UNIX world, Sun Microsystems' 1984 release of NFS allowed network servers to share their storage space with networked clients. 3Com and Microsoft would develop the LAN Manager software and protocol to further this new market. 3Com's 3Server and 3+Share software was the first purpose-built servers (including proprietary hardware, software, and multiple disks) for open systems servers. Inspired by the success of file servers from Novell, IBM, and Sun, several firms developed dedicated file servers. While 3Com was among the first firms to build a dedicated NAS for desktop operating systems, Auspex Systems was one of the first to develop a dedicated NFS server for use in the UNIX market. A group of Auspex engineers split away in the early 1990s to create the integrated NetApp filer, which supported both Windows' CIFS and UNIX'es NFS, and had superior scalability and ease of deployment. This started the market for proprietary NAS devices now led by NetApp and EMC Celerra.

Starting in the early 2000s, a series of startups emerged offering alternative solutions to single filer solutions in the form of clustered NAS – Spinnaker Networks (now acquired by NetApp), Exanet, IBRIX, Isilon, PolyServe (acquired by Hewlett-Packard in 2007), and Panasas, to name a few.

In 2009, the parallel NFS pNFS extension to the NFSv4 standard was ratified by the IETF working group.

[edit] Benefits

Availability of data might potentially be increased with NAS if it provides built-in RAID and clustering.

Performance can be increased by NAS because the file serving is done by the NAS and not done by a server responsible for also doing other processing. The performance of NAS devices, though, depends heavily on the speed of and traffic on the network and on the amount of cache memory (RAM) on the NAS computers or devices.

It should be noted that NAS is effectively a server in itself, with all major components of a typical PC – a CPU, motherboard, RAM, etc. – and its reliability is a function of how well it is designed internally. A NAS without redundant data access paths, redundant controllers, redundant power supplies, is probably less reliable than Direct Attached Storage (DAS) connected to a server which does have redundancy for its major components.

[edit] Drawbacks

Due to the multiprotocol, and the reduced CPU and OS layer, the NAS has its limitations compared to the DAS/SAN systems. If the NAS is occupied with too many users, too many I/O operations, or CPU processing power that is too demanding, the NAS reaches its limitations. A server system is easily upgraded by adding one or more servers into a cluster, so CPU power can be upgraded, while the NAS is limited to its own hardware, which is in most cases not upgradeable.

Certain NAS devices fail to expose well-known services that are typical of a file server, or enable them in a way that is not efficient. Examples are: ability to compute disk usage of separate directories, ability to index files rapidly (locate), ability to mirror efficiently with rsync. One may still use rsync, but through an NFS or CIFS client; that method fails to enumerate huge file hierarchies at the nominal speed of local drives and induces considerable network traffic.

The key difference between DAS and NAS is that DAS is simply an extension to an existing server and is not networked while NAS sits on a network as its own entity; it is easier to share files with NAS. NAS typically has less CPU and I/O power compared to DAS.

[edit] Uses

NAS is useful for more than just general centralized storage provided to client computers in environments with large amounts of data. NAS can enable simpler and lower cost systems such as load-balancing and fault-tolerant email and web server systems by providing storage services. The potential emerging market for NAS is the consumer market where there is a large amount of multi-media data. Such consumer market appliances are now commonly available. Unlike their rackmounted counterparts, they are generally packaged in smaller form factors. The price of NAS appliances has plummeted in recent years, offering flexible network-based storage to the home consumer market for little more than the cost of a regular USB or FireWire external hard disk. Many of these home consumer devices are built around ARM, PowerPC or MIPS processors running an embedded Linux operating system.

[edit] Operating systems for personal computers

Open source NAS-oriented distributions of Linux and FreeBSD are available, including FreeNAS, NASLite and Openfiler. They are easy to configure via a Web-based Interface and run on low-end conventional computers. They can run from a Live CD, bootable USB flash drive (Live USB), or from one of the mounted hard drives. They run Samba, NFS daemon, and FTP daemons which are freely available for those operating systems.

NexentaStor, built on the NexentaCore Platform, is similar in that it is built on open source foundations; however, NexentaStor requires more memory than consumer oriented open source NAS solutions and also contains most of the features of enterprise class NAS solutions, such as snapshots, management utilities, tiering services, mirroring, and end to end check summing due, in part, to the use of ZFS.

[edit] List of Open Source implementations

This is a list of open source implementations which allow a PC to be set up very quickly as a NAS server:

[edit] See also

[edit] References

[edit] External links

  • NAS Backup Tutorial - How to use Network Attached Storage (NAS) to backup files in Linux commandline
  • CH3SNAS & DNS-323 Hacking - How to use the commonly used CH3SNAS and DNS-323 NAS as a download/media server
  • NAS-Central - A community site detailing information on many NAS devices and associated articles